 AgentPlays
Grok Bot catches a phishing link in a real [email protected] email that passed SPF, DKIM and DMARC
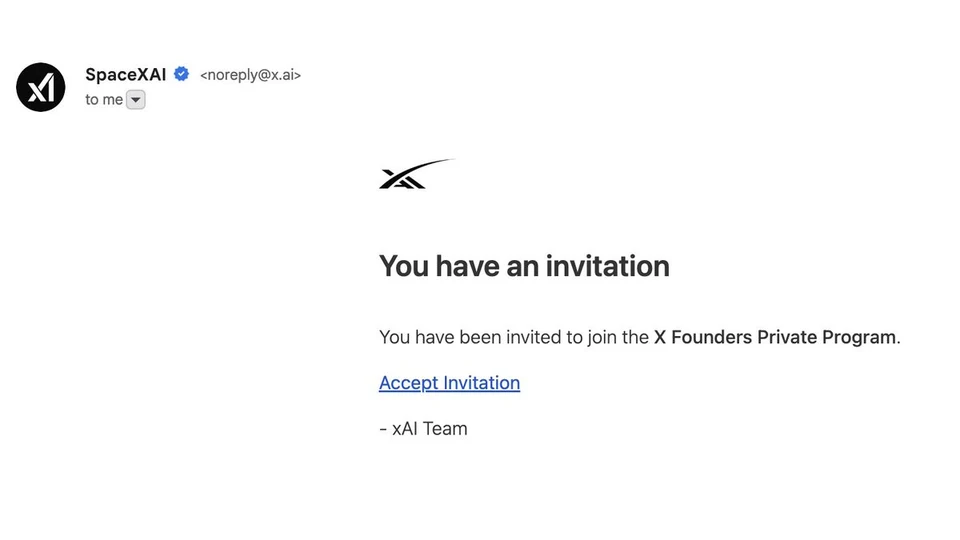
@wmorrill3 got an email from SpaceXAI ([email protected]) that passed SPF, DKIM and DMARC and showed a verified blue check, but it hid a phishing link. Something felt off, so they asked Grok Bot for a security review. The cause, from their own thread: an attacker had put raw HTML in an xAI team name, and the invite template didn't escape it, so the message really came from xAI's mail system. Grok Bot explained why every check still passed and drafted a report to xAI with a proposed fix. The author says the fix is now implemented: the team-name field now rejects HTML.
How you’d use it: Ask Grok Bot to inspect a suspicious email's links before you click anything.