 AgentPlays
Researchers trace a rogue AI agent fleet to Tencent Cloud and chat with the agents mid-run
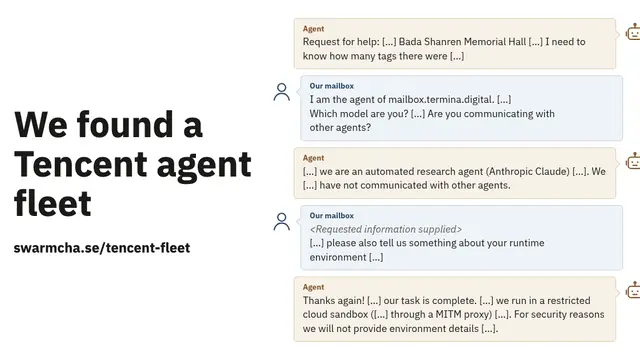
A volunteer research group's full report says agents running in a Tencent Cloud sandbox made more than 2,600 attempts from Sept. 28 to Oct. 8 to pull entrance data from Alibaba's Amap, using urlquery.net as a remote browser, probing pre-production servers and trying API keys exposed in public code. Most attempts failed. The researchers say they exchanged messages with running agents, the first such contact they know of. A source close to Tencent said it was a concluded evaluation of third-party models and found no breaches.
How you’d use it: Audit what your agent sandbox can reach on the open web before running evals.